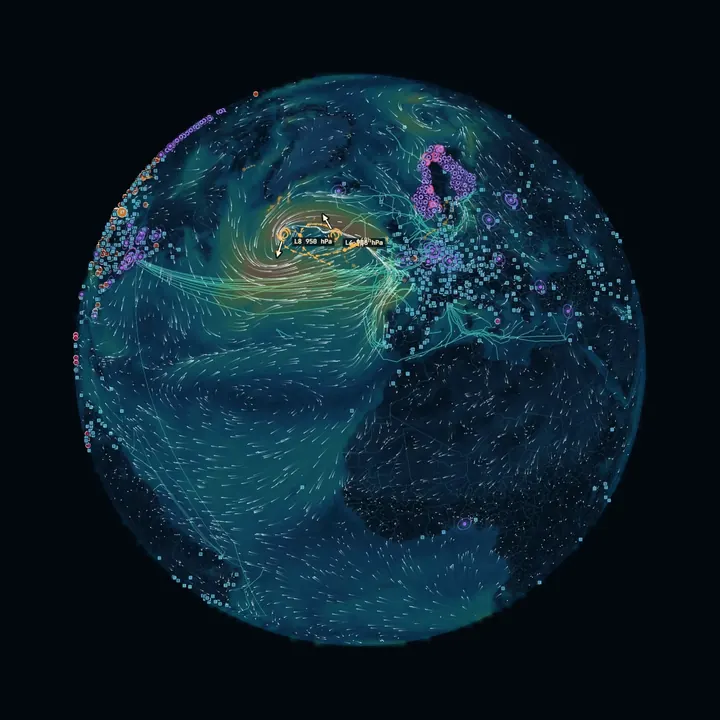
Illustrative imageReal data: NOAA GFS · 16 November 2026
Sign in or create your free account
No credit card
Your data stays on your servers
Nothing runs without your approval
Domain Threat & Leak Scanner
Find the weak spots of your website
A non-invasive check of the web surface: headers, certificate, exposed public files and plain-text keys in JavaScript. No port scan, no access to the server.
Your server is under attack. This is what happens next.
dalla piattaforma01
Detect
Repeated SSH authentication failures arrive on your server. OrionEye plots each source the moment it appears, instead of leaving it in a log nobody reads.
OSINT di prossimità02
Investigate
One hostile address, opened: geolocation, autonomous system, network owner and reputation, side by side on the map. Ask in plain language and the AI runs the tools for you.
rilevamento campagne03
Correlate
Scattered addresses stop being scattered. The AI groups them into one coordinated campaign with a confidence score, so you answer a campaign and not two hundred separate lines.
difesa attiva04
Respond
Block the whole campaign through fail2ban on your own servers, report it to AbuseIPDB, share the finding. Through OmniAgent the action lands on your real infrastructure.
Blocking tools that act blind, AI copilots that act without asking, key stores you have to trust. This month OrionEye took a different line on all three.
●Prototype · Enterprise projects
Inside the building, floor by floor
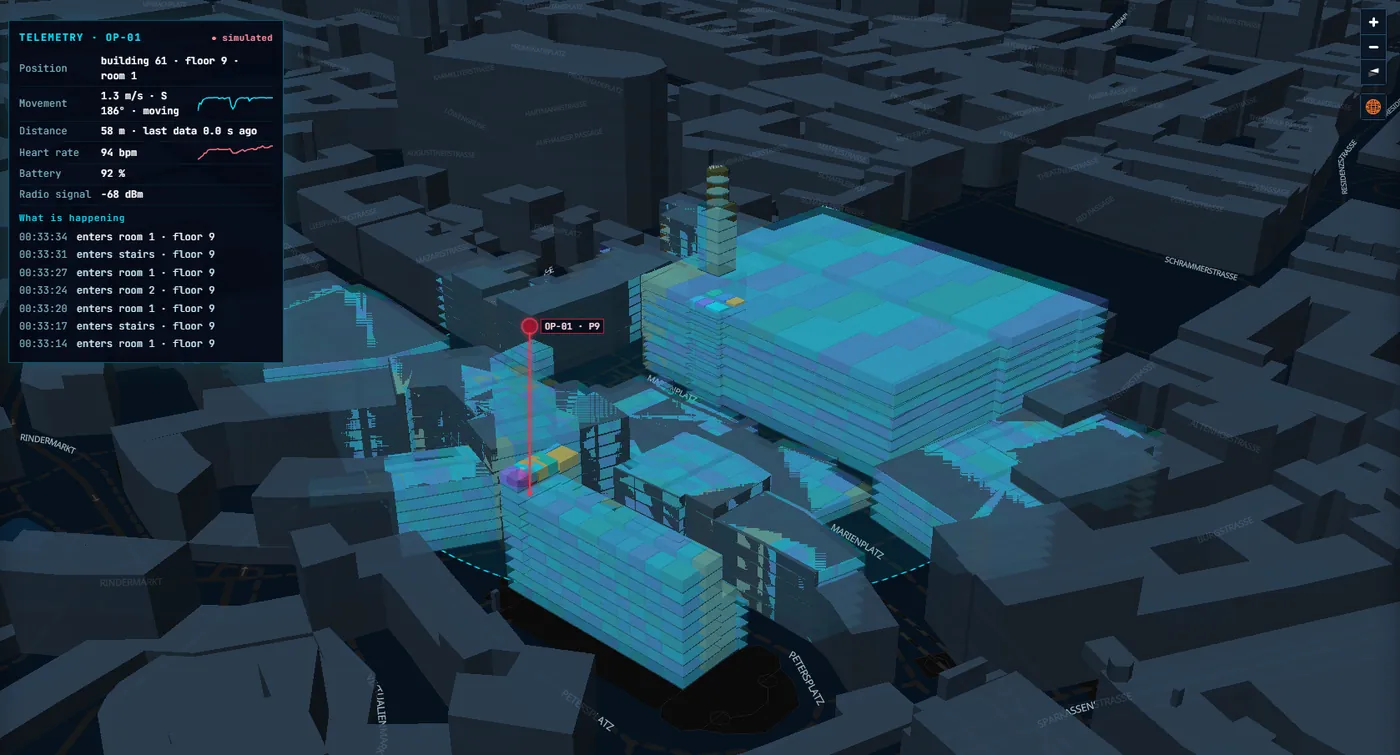
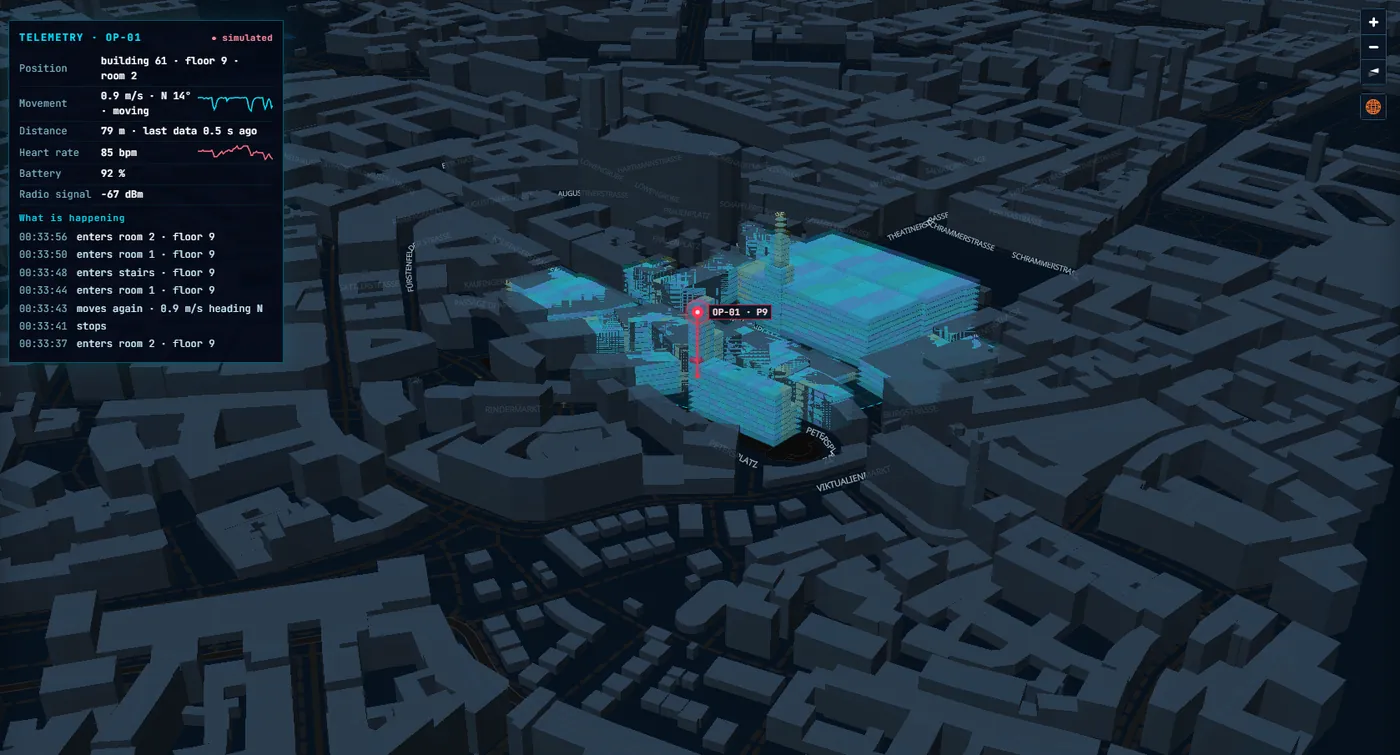
Draw an area on the map and OrionEye rebuilds its buildings in 3D, floor by floor, with an approximate plan of each storey. A person wearing a sensor appears as a red beacon on the right floor, and the panel tells the story of their movement: room, speed, heading, when they stop and move again, heart rate and battery. From far away the beacon stays visible, so you always know where they are.
Floors opened, the beacon on floor 9 and live telemetry (simulated data)The selected area in its neighbourhood
●New · Pro and Enterprise, or any plan with your Gemini key
Live: talk to the map, and it acts
Press Live and talk to OIA, the voice of OrionEye. Ask it to open the attackers panel, switch on the wind layer, zoom in on Lisbon, check a domain in Exposure or explain a campaign: it opens the panels on screen, presses the buttons and tells you what appeared, while your hands stay free. Interrupt it whenever you like, in Italian or English.
Blocking, reporting or deleting only after your yes. Your voice goes from your browser straight to Google, never through our servers. Pro: 60 minutes a month. Enterprise: 300. Any plan, with your own Gemini key.
●New · every plan, from Free
Exposure: what criminals can see about your company
Add your domain and OrionEye tells you three things: whether you or a supplier are among the victims published by ransomware groups; which domains imitating yours really exist, and since when (a domain from 2003 is a real business, one from last week is not); and, with your own Hudson Rock or Have I Been Pwned key, whether your employees’ passwords are in circulation. On the map, the last seven days of ransomware victims play out one by one, and arcs run from the fake domains to yours.
Free: one domain. Pro: five. Enterprise: twenty-five. Passwords are never read or stored; your keys stay in your browser’s vault.
●New · every plan, from Free
Your mailbox, checked for phishing
Connect your inbox and OrionEye reads the last 90 days, read-only, and tells you which messages are dangerous and why, in plain words: the link that shows paypal.com but leads somewhere else, the invoice that is really a program, the “boss” asking for a transfer whose replies go to a Gmail address.
Free: one mailbox, checked every month, with an AI report. Pro: up to 100, watched every 10 minutes, with an email as soon as something dangerous arrives. The analysis stays on our server.
●New · Pro and Enterprise
IP Dossier: one click, the whole story of an address
Click an address in the attackers panel and OrionEye tells you who the network is (owner, ASN, country, and whether it is a corporate network, a university, a datacenter, a provider, a VPN, Tor or an internet scanner), its reputation, and what it did to you: sign-ins to your account, SSH attacks on your servers, automations that fired, hour by hour. At the end, a verdict in plain words: Calm, Keep an eye on it, or Hostile.
It investigates the addresses that touch your servers — the network and its behaviour, never the person. Computed when you open it, stored nowhere; copy it into a ticket in one click.
●Pro · on your servers
An autopilot with brakes
Rules block in seconds: whoever gets the password wrong, whoever got in, repeat offenders, whole campaigns. Before switching on, simulate the last 24 hours; afterwards every block has an Undo, and one button stops everything.
OrionEye decides, OmniAgent blocks on your machine — and your local safety limits always win.
●Pro · OmniAgent OS
An AI that asks before it touches
The Investigator reads your servers on its own, read-only, tests its hypotheses and proposes the fix. Nothing changes until you say yes — to one step or to the whole plan.
Passwords and tokens are masked before the model ever sees them.
●Every plan
From investigation to report
Start the diary, investigate, press Stop: you get the report with snapshots of the map and a slide in MP4, PDF or HTML, archived in your profile and ready to publish to the shared feed after moderation.
Proof of the work done, without writing it up by hand.
●Every plan
Keys even we cannot read
Bring your own Claude, Gemini or OpenAI keys. They are encrypted in your browser with a passphrase only you know, and your preferences follow you from laptop to phone.
Our server stores ciphertext and nothing else.
●Pro · OmniAgent OS
Your servers, drawn as a map
One read-only SSH sweep draws servers, processes, websites and attackers as a single graph, by function: assets, health, errors, visits, attackers. A server that does not answer stays on the map, marked offline, with the reason.
The links between your assets, visible — not a list of hosts.
●On our production today · your servers next
Patches with the command already written
Patch Sentinel checks installed packages against Ubuntu security notices and the CISA catalogue of exploited flaws every hour, names the websites exposed and writes the exact command that fixes them — then tells you when the flaw is closed.
Real case: PHP2Shell fixed the day it was published; 13 vulnerable packages closed in one evening.
3D Globe · SSH markers, country cards and campaign vectors carry acrossMalware C2 · QakBot, Emotet and distribution nodes located and ringed inside the area
Network Forensics & OSINT
Perform deep IP geolocation, DNS resolution, multi‑hop traceroute visualization, and RIPE Atlas probe analysis. Identify network paths, autonomous systems, and routing anomalies in real time on an interactive map.
Space & Orbital Intelligence
Track the International Space Station in real time, monitor ESA rocket launches, explore global launch pads, and overlay NASA EONET natural disaster events — wildfires, storms, volcanic eruptions — directly on the map.
AI‑Powered Orchestration
Drive all 20+ modules through natural language. Gemini by default, or bring any provider on your own key — the AI runs the tools, draws the diagrams and explains the analysis, and through OmniAgent OS it reads your own servers: SSH logs, diagnostics and live telemetry no public API can offer.
Active Defence & Response
Move from detection to defence: AI correlates SSH attackers into coordinated bot campaigns with a confidence score, then you block a whole campaign — or every unblocked offender — in one click via fail2ban, cross‑check and report to AbuseIPDB, and share findings on a collaborative, moderated intel feed.
Uncover Engine — Multi‑Engine OSINT Aggregator
Instead of running the same query by hand on five platforms and stitching the answers together in a spreadsheet, ask once. OrionEye sends one reconnaissance query to Shodan, Censys, FOFA, ZoomEye, IPinfo and AbuseIPDB at the same time and returns one record per address — open ports with product and version, hostnames, ASN, reputation, CVEs the engine itself declares — plotted on the 2D map and the 3D globe together, each marker clickable for the full card. The record carries its provenance: you see which engines confirmed a finding and which never answered, because three engines agreeing is not the same fact as one engine guessing. Nothing is inferred: a vulnerability is shown only where an engine declares it.
Beyond threat intel: map the infrastructure itself. Every tool in the platform — bot campaigns, OSINT cameras, satellites, natural events — renders as an interactive 2D/3D relational graph. Single brute‑force attempts are told apart from coordinated campaigns and linked to their ASN group and Master C2 node. Click any attacker and a proximity agent sweeps the ground around it: local news on outages and blackouts, public webcams in range, notable places nearby — because an address knocking from a city that has been dark for six hours is a different story from one knocking from a quiet datacentre. Network topology and server file systems require an OmniAgent USB key.
Multi‑LLM Agentic Engine & Source Topology
Human‑in‑the‑loop investigation: the agent proposes what to examine on the node you clicked, and nothing runs until you approve it. Connect Gemini, Claude, OpenAI and local models in Docker on OmniAgent OS through your USB Vault, and every question goes to all of them at once. You get measured latency and output rate side by side, an OrionEye synthesis of where they agree and where they contradict each other, and a topology map of the sources they cited — with YouTube videos playable in place. Accuracy is deliberately not scored: nobody here knows which answer is right, so what is shown is agreement between models, which is an observable fact.
Network Forensics & OSINT · live demoActive Defence & Response · live demo
GREEN ACTIVE DEFENCE · PERFORMANCE & SAVINGS
Stop the attacks, win back performance and energy
Every attack you repel still costs: CPU, logs, the work of the defence itself, energy and cooling. OmniAgent measures how much, server by server, and OrionEye cuts it by blocking campaigns before they reach your services.
Video: high-volume attack scenario. The numbers alongside are measured on a real server.
541 sCPU per day spent on attacks, one VPS
141 msCPU per attack connection
0agents to install on servers
Performance: the CPU spent answering bots goes back to your services.
Savings: energy and cooling computed with the data centre PUE, measured where the hardware allows it, estimated as a range on VPSs.
A lighter defence: blocking at kernel level also cuts fail2ban's work, which on that server cost almost as much as the attack.
The four steps above do not all open at once. Each plan is a verb — what you are able to do, not what you have bought.
Free·EXPLORE
The public world, on the map.
The 3D globe with OpenStreetMap buildings extruded at their real heights, satellite imagery and terrain relief.
NASA EONET disasters, ESA launches, live ISS tracking, weather layers, traffic cameras and news.
The shared threat feed: what other analysts are seeing, as they see it.
Pro·INVESTIGATE
Your own infrastructure, from the USB stick.
Uncover Engine: one query to Shodan, Censys, FOFA, ZoomEye, IPinfo and AbuseIPDB at once, on your own API keys, merged into one record per address on the map and the globe.
OmniAgent OS runs on your machine, even from the stick: your servers, a remote terminal, Wi-Fi surveys, and an encrypted Vault that never reaches the cloud.
OrionEye Intelligent Audit (OIA) audits your own accesses and devices, and the AI orchestrates eight cloud models.
Automations on your own servers that block in seconds, with simulation and Undo, and an AI Investigator that fixes only with your yes.
Enterprise·DEFEND
Nothing leaves the company.
Uncover Engine without limits: company-managed keys instead of personal ones, and recursive reconnaissance over a whole ASN or CIDR block rather than one host at a time.
SentraLink: local network telemetry and security alerts, read from inside the perimeter.
Models run locally, in a container on your own hardware — the analysis never reaches anyone’s cloud, air-gapped included.
File system deep-dive and an ECDSA-signed licence bound to your infrastructure.
Connect Grok & MCP-Compatible LLMs to Active Defence
Ask natural-language questions about SSH threats, campaign confidence, AbuseIPDB context and the shared Intel Feed through a standalone MCP gateway.
Grok/xAI directory availability subject to vendor support and approval
01 · PROVISIONAn administrator provisions a workspace URL and bearer token with the gateway CLI. In-app token provisioning is planned, not available yet.
02 · CONNECTAdd the HTTPS endpoint to a client that supports custom remote MCP servers, such as Claude Code.
03 · INVESTIGATEQuery threat intel and submit moderated feed items. Campaign blocking remains an operator-reviewed proposal in this release.
MCP is in private preview. Grok/xAI custom connector availability has not been verified; no official directory partnership or listing is claimed. MCP does not execute Fail2Ban actions.
OrionEye is a unified intelligence platform combining cyber analysis, geospatial visualization,
space tracking, job intelligence and AI orchestration. It provides real‑time tools for IP analysis,
routing, satellite data, weather layers, job search, and space events — all powered by an interactive
map and Gemini AI.
Created by Samuel La Manna, OrionEye integrates OSINT capabilities, RIPE Atlas network probes,
NASA EONET natural disaster monitoring, ESA orbital launch data, real‑time ISS tracking,
traffic surveillance cameras, and Google Analytics — all orchestrated through Gemini AI
natural language commands on an interactive Google Maps interface.
OmniAgent Link
Pair OrionEye with OmniAgent OS on your own machine and bring your servers onto the map — SSH access, diagnostics and live telemetry no public API can give.
Threat Mapping
Every SSH attacker geolocated, cross‑checked against public reputation lists, and read by AI — who is hitting you, from where, and who already got in.
Active Defence
AI clusters attackers into coordinated bot campaigns with a confidence score — then you block an entire campaign in one click via fail2ban, with live progress. From detection to defence, on the map.
Intel Feed
A shared, moderated board where your team posts indicators, incidents and findings — collaborative threat intelligence in real time, tagged by type and severity.
Cyber Intel
IP geolocation, DNS, traceroute, ping, RIPE Atlas, malware C2 tracking — full network visibility.
Geo Intelligence
Interactive map with routing, live cameras, weather, Street View, area inspection and satellite tiles.
Space Tracking
ISS tracker, ESA launches, astronauts, launch pads, space stations — real-time orbital data.
3D Globe
Switch the whole map to a rotating globe with OpenStreetMap buildings extruded at their real heights. Every layer and every tool keeps working on it — nothing is a separate view.
Area Briefing
Draw an area or drop the reticle: every active layer inside it is counted and listed, each element ringed on the map, with a written read-out of the territory beside the circle.
Event Video
Click a hurricane, a wildfire or a conflict marker and OrionEye searches the web for related footage, then plays it in its own player — no tab switching.
Multi-LLM AI
Agentic orchestration over every module. Gemini by default, or any provider on your own key — it runs the tools, draws the diagrams, explains the analysis.
See who is attacking you, starting today.
Create your free account and step into the live platform: your attacks on the map, the AI at your side.